
Endpoint detection & response
Use high-fidelity endpoint telemetry, AI-powered protection, detection, investigation, and response.
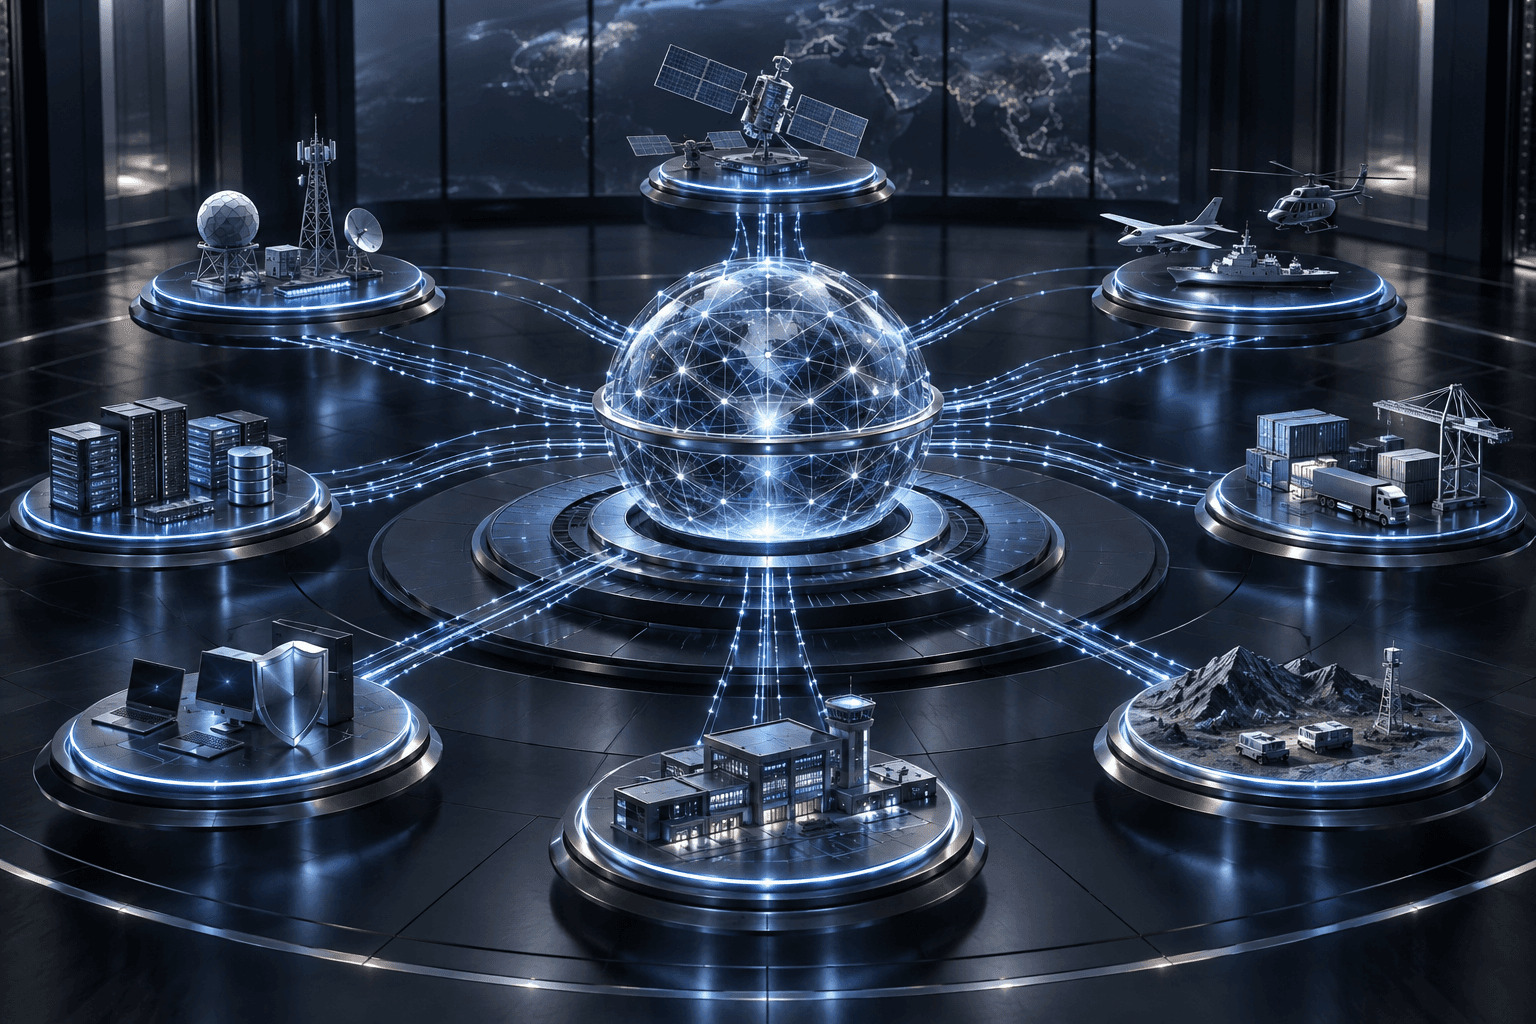
Turn fragmented signals into decision-ready intelligence.
ExploreTurn Falcon detections, incidents, assets, identities, and threat intelligence into mission-aware decisions.
The CrowdStrike Falcon® platform combines security data, adversary intelligence, AI, automation, and expert services on a unified architecture. It provides visibility and protection across endpoint, identity, cloud, SaaS, data, and AI systems, with a documented API surface for alerts, detections, incidents, event streams, assets, exposure, and intelligence.
Use high-fidelity endpoint telemetry, AI-powered protection, detection, investigation, and response.
Correlate threats across identities, workloads, applications, data, and cloud environments.
Enrich investigations with adversary context, indicators, intelligence feeds, and expert hunting.
Programmatically access alerts, detections, hosts, incidents, exposure, intelligence, and streaming events.
A governed SAM™ connector can ingest authorized Falcon alerts, detections, incidents, event streams, asset context, and intelligence through documented APIs. SAM™ then correlates those cyber signals with operational, physical, supply-chain, and mission dependencies so teams can prioritize what matters, explain why, and route the right response without replacing Falcon workflows.
Best suited forRank Falcon incidents by the business services, facilities, suppliers, or missions connected to affected assets.
Place endpoint and identity evidence beside physical, operational, and supply-chain signals on one timeline.
Translate technical detections into accountable risk decisions, owners, actions, and consequence narratives.