
Why the Speed of Security Decisions Determines Outcomes
In security, outcomes are rarely determined by whether an event is detected. They are determined by how quickly and effectively decisions are made after detection.
Across cybersecurity, physical security, fraud prevention, and critical infrastructure protection, organizations have invested heavily in technologies that increase visibility into their environments. These investments have dramatically improved detection capabilities. However, detection alone does not stop incidents.
Security outcomes are determined by decision velocity—the speed at which organizations can interpret signals, prioritize threats, and initiate appropriate responses.
Executive Summary
Today, most security architectures optimize for signal generation, not decision velocity.
The result is a growing operational challenge: security teams are receiving more alerts than ever before while their ability to convert those alerts into timely decisions has not kept pace. This imbalance creates what can be described as the Security Decision Velocity Problem.
Solving this problem requires a new architectural approach to security systems—one that prioritizes decision-support infrastructure capable of accelerating and improving the quality of security decisions.
Detection Is Not the Bottleneck
In modern security environments, the primary technical challenge is no longer detection. Organizations have deployed extensive detection infrastructure, and these systems are highly effective at identifying signals that may represent risk.
The bottleneck emerges after detection occurs. These are decision-making tasks, not detection tasks. As detection systems improve, the number of signals requiring interpretation increases. Without corresponding improvements in decision infrastructure, the result is operational overload.
- Endpoint monitoring tools
- Network security platforms
- Surveillance and access-control systems
- Threat intelligence feeds
- Anomaly detection algorithms
- Determine whether an event is a real threat, its potential severity, whether action is required, and who should respond
The Cost of Slow Security Decisions
Security incidents often follow predictable escalation timelines. A vulnerability becomes an exploit. An anomaly becomes an intrusion. A suspicious activity becomes a breach.
At each stage, organizations have opportunities to intervene. The effectiveness of these interventions depends on how quickly decisions are made.
In many cases, organizations detect incidents early but fail to act quickly enough to prevent escalation. The difference between a contained event and a major incident is often measured in minutes or hours. Decision velocity therefore becomes a critical factor in security outcomes.
- Delayed containment of cyber intrusions
- Prolonged operational disruption
- Increased financial loss
- Reputational damage
- Regulatory exposure
Why Decision Velocity Breaks Down
Several structural issues within modern security environments contribute to slow decision-making.
Fragmented information: cybersecurity data, physical security telemetry, financial intelligence, and operational data often exist in separate systems. Analysts must manually synthesize information before making decisions.
Alert fatigue: SOC teams may receive thousands of alerts per day. Manual triage slows decision cycles and increases the risk of missed threats.
Context deficiency: many alerts lack the contextual information needed to assess risk. Analysts must conduct additional investigations before making decisions.
- User role
- Geographic location
- Associated network activity
- External threat intelligence
Measuring Decision Velocity
Decision velocity can be understood as the time required to move from signal detection to operational action. In many organizations, the majority of time is spent in signal correlation, risk prioritization, and decision formation.
Improving decision velocity therefore requires reducing the friction between signal detection and decision formation.
- Signal generation
- Signal correlation
- Risk prioritization
- Decision formation
- Response initiation
Decision Support as a Strategic Capability
Security leaders increasingly recognize that improving detection accuracy alone will not solve operational challenges.
Instead, organizations must develop systems that help security teams answer key operational questions faster. These questions require systems capable of analyzing data across domains and presenting actionable insights.
This capability represents the emerging field of Security Decision Intelligence.
- What matters most right now?
- Which threats require immediate action?
- What are the likely consequences of different response options?
Toward Faster Security Decisions
Future security architectures must incorporate technologies that accelerate decision cycles. These functions help security teams move from reactive alert processing to proactive decision-making.
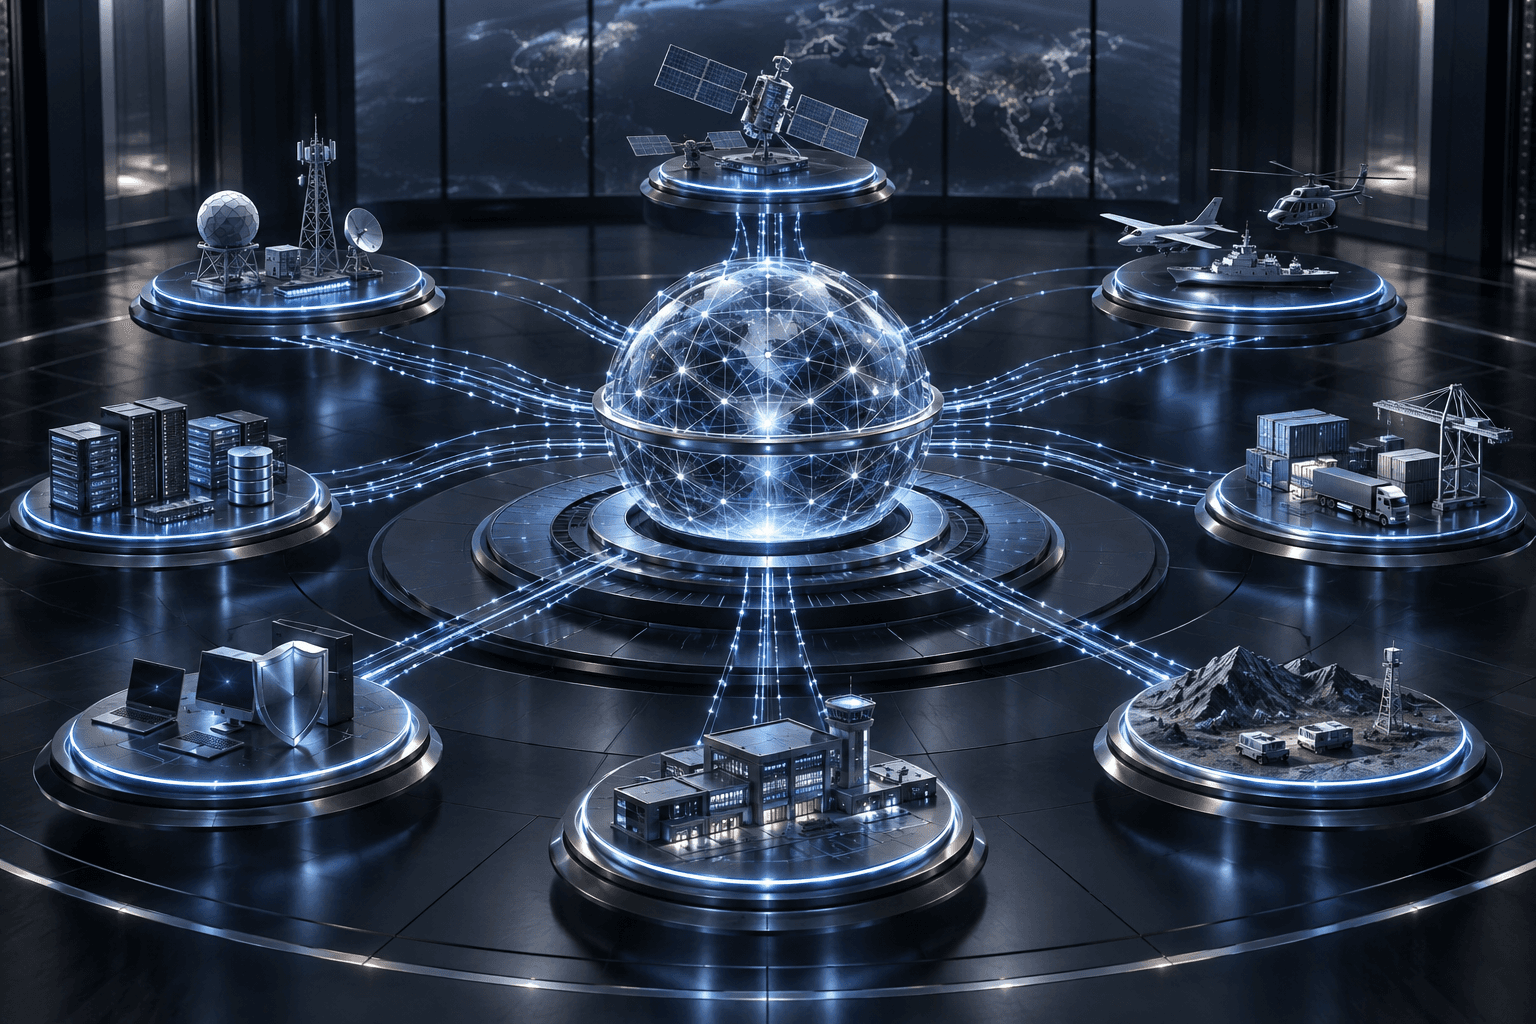
One emerging approach involves integrated intelligence layers capable of synthesizing signals across multiple security systems. This type of architecture can significantly reduce the time required to interpret signals and initiate responses.
An example is a security analytics mesh, which integrates diverse security data sources and applies advanced analytics to support operational decisions.
- Cross-system signal correlation
- Dynamic risk prioritization
- Predictive analytics
- Scenario modeling
Conclusion
Security incidents are not prevented by detection alone. They are prevented by fast, informed decisions.
As security environments continue to generate increasing volumes of data, the ability to make rapid, well-informed decisions will become one of the most important capabilities in modern security operations.
Organizations that improve decision velocity will gain significant advantages in risk management and operational resilience. Achieving this improvement will require new architectural approaches focused on decision intelligence infrastructure.